The business problem
A business team wants a complete view of work across sales and service. Copying every record into a shared workspace would expose information that some collaborators do not need. A useful overview must retain meaningful boundaries.
Design the management relationship
Define access by business role, purpose and responsibility. Share the minimum context needed for a handoff, while recording who can view, change and approve each item. Test effective access rather than relying on the visual appearance of a filtered page.
Build the structured operating model
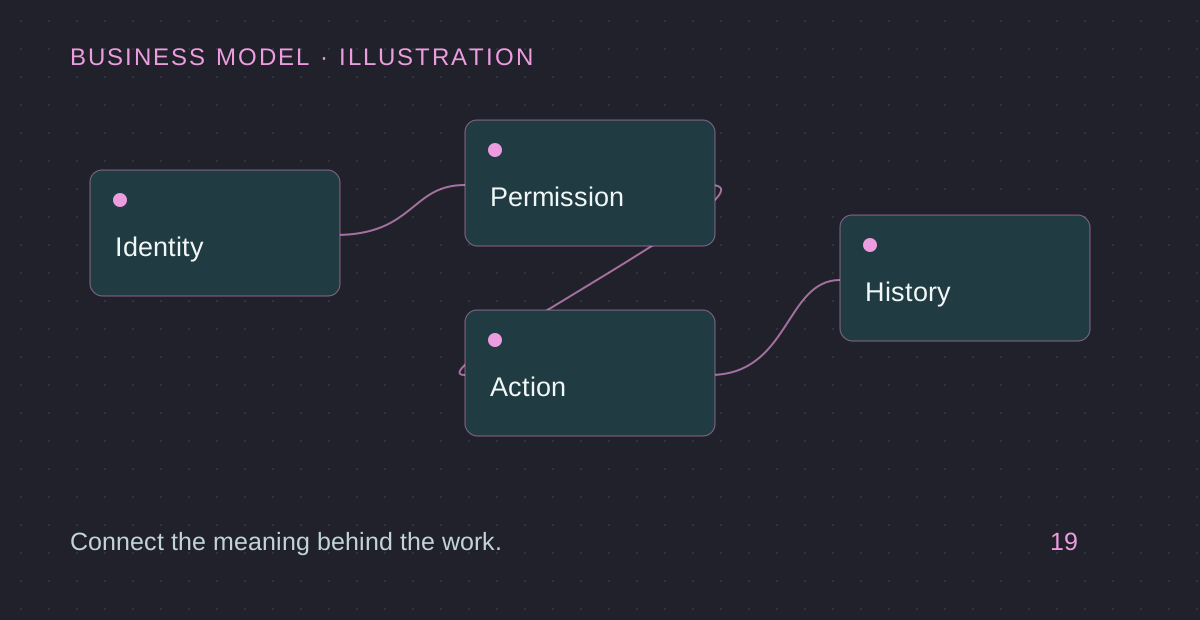
Define authority using role, business object, action and context. Viewing a summary, changing a request and authorizing external communication are separate permissions. Apply the same discipline to agents and people, including delegated authority and revocation. A filtered screen is not an access boundary. Test intended and unintended actions with representative identities and synthetic information. The business owner should understand who may act on whose behalf, while implementation validates that those boundaries hold across connected systems.
The decision for your role
For a CIO, this capability must preserve meaning and authority across systems. Identify which application owns each business fact, which identity performs an action and which role is accountable for its result. A successful transfer of information does not establish a successful business handoff. Compare the state definitions used on each side and decide how disagreements become reviewable exceptions. Keep access rights distinct from screen filters, and distinguish permission to prepare work from permission to change a business system or communicate externally. The operating model should also identify disconnected sources and observation gaps so an incomplete overview is not mistaken for full visibility. Introduce connections in a bounded sequence with representative identities and synthetic information. Test a normal path, an access denial, a stale event and a failed handoff. Give support and recovery duties explicit owners. This allows business managers to govern the purpose and responsibilities while technical teams validate that the intended controls and information flows work in practice.
Apply it in the operating setting
For an illustrative insurance operations scenario, separate the information needed to coordinate work from information restricted to an authorized role. A summary can state that a review is pending without revealing the underlying detail. Test whether connected views preserve the same boundaries as the source process, including when an agent acts on behalf of a user. Record the business purpose of access and how it ends. The example concerns operational design; it does not establish compliance or suitability for regulated decisions. Use synthetic cases during validation and have the appropriate organizational owners define the actual information and approval requirements.
The operating discipline
A governance control is useful when people understand its purpose, authority and exception path. Define the business object being controlled, the person accountable for it and the evidence that demonstrates the control worked. Keep the current state distinct from the history of how it changed. An AI suggestion should remain distinguishable from an authorized decision. Test the arrangement with realistic permitted and denied actions, and include a failure case. Documentation alone does not show that an access boundary, approval or recovery process works in practice.
A practical decision example
An operations overview might show that a request is awaiting an authorized review without exposing the underlying restricted information. Design the summary and its permitted detail separately. Test access using the actual intended roles, including users who belong to more than one team. A convenient shared overview should help people coordinate while keeping the sensitive business context within its agreed audience.
Observe, automate and verify responsibly
Before enabling an automatic action, define what the operating history must retain. A useful record identifies the actor, business object, time, reason, authority, relevant input version, observed action and resulting state. Keep a failed attempt separate from a successful retry. If the action sends an email, distinguish preparation, approval, send attempt and delivery observation; attempting to send does not prove that the recipient received or acted on it. Assign an owner for exceptions and say when a human must intervene. Then ask a colleague who was not involved to reconstruct the event using the records alone. Missing context is a model gap to resolve before increasing autonomy. This is how observability supports accountability across people, agents and connected systems, rather than becoming a large collection of unexplained technical logs.
What to test first
Use representative roles and synthetic records to test boundaries. Record unexpected access and blocked legitimate work. The example describes governance design, not an insurance compliance certification.
What this means for Flowise
Flowise is designed around a shared company model: business purpose, relationships, ownership, and results. Start with real work, preserve the supporting evidence, and improve the model as the team learns.